Web application firewalls (WAFs) only filter incoming traffic. Browser-enforced security headers provide essential defense-in-depth by commanding the visitor's browser to block unauthorized script execution (CSP), refuse iframe embedding (clickjacking prevention), and enforce strict TLS transport (HSTS).
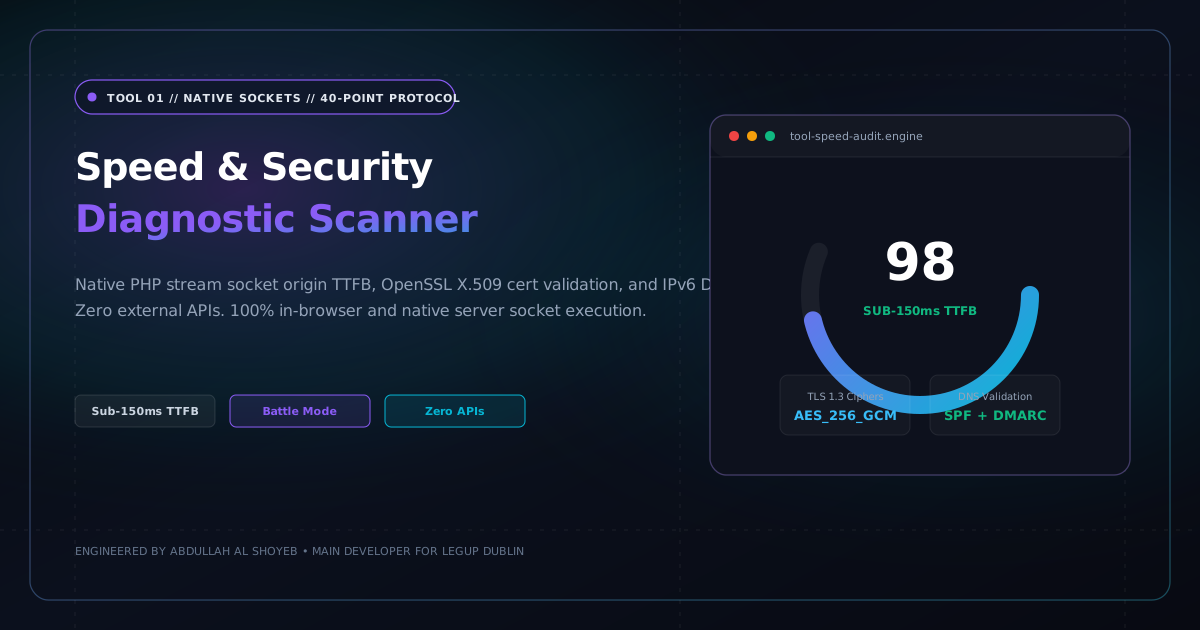
40-Point Speed, Security & Competitor Battle Scanner
Direct origin socket benchmarking, native OpenSSL X.509 cert inspection, authoritative SPF/DMARC DNS tests, and head-to-head competitor battle mode.
Launch Tool Studio →